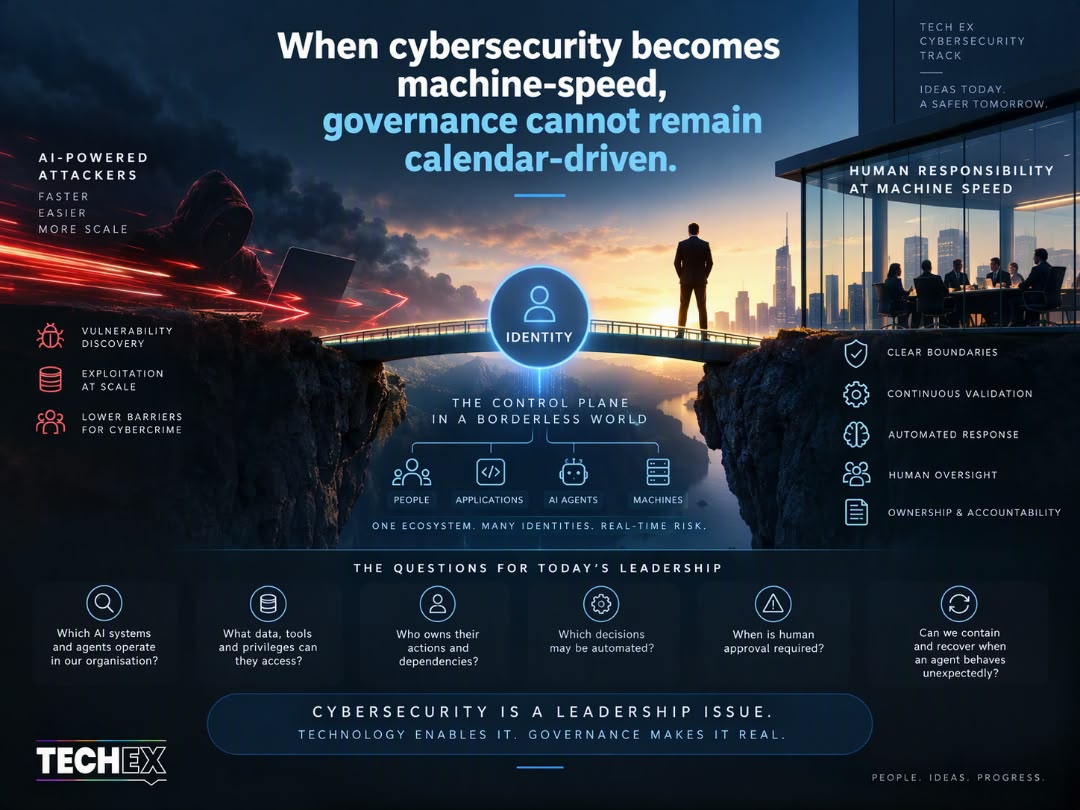
That may sound obvious. After following the cybersecurity track at TechEx yesterday, I think the reason why is becoming more important.
It is not because boards should take responsibility for technology.
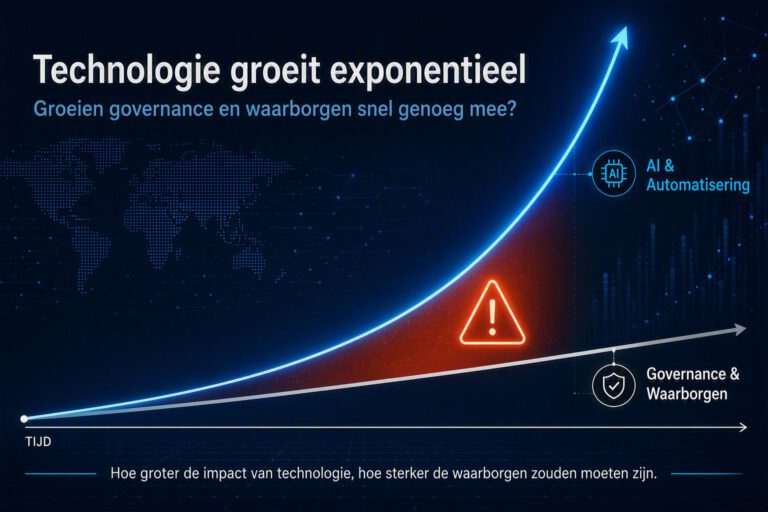
It is because technology increasingly makes decisions and takes actions that create business risk.
AI accelerates that development. AI agents can access information, interact with systems and increasingly perform tasks with a degree of autonomy.
So the questions for leadership change:
What are we willing to automate?
What are we willing to trust?
Where do we demand human accountability?
And are we prepared for the moment when something goes wrong?
Those are not questions for the CISO alone.
Identity security, continuous monitoring, automated response and clear boundaries provide the technical foundation. But technology cannot decide an organisation’s risk appetite or establish accountability.
That requires governance.
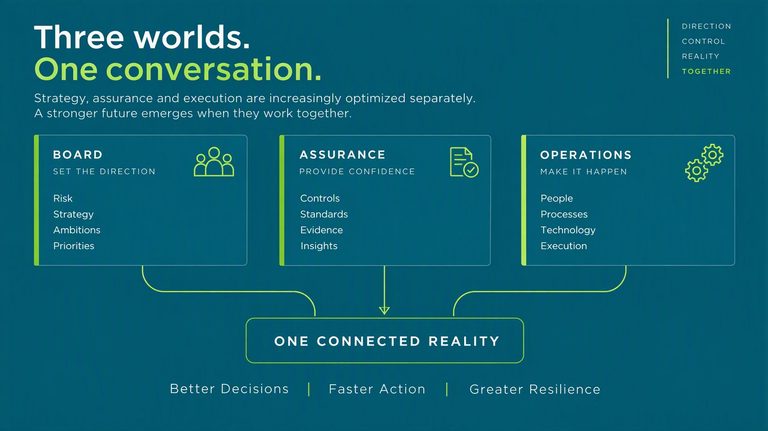
The board doesn’t need to know how every security control works.
It does need to know what the organisation is protecting, what risks it is accepting, who is accountable, and whether the business can recover when prevention fails.
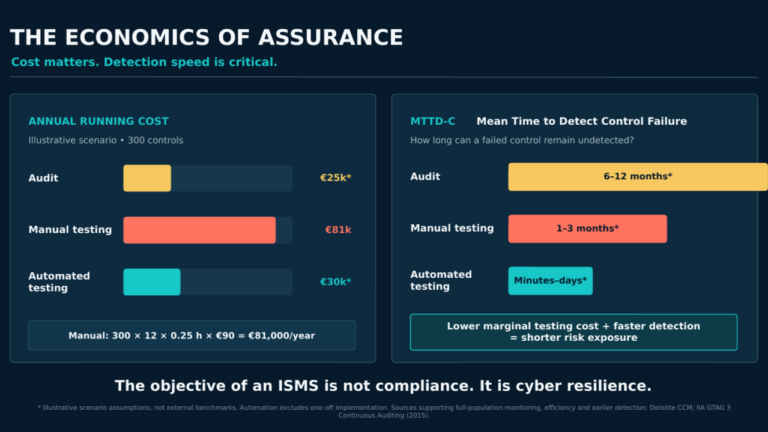
For me, that is increasingly what cyber resilience is about.
Not just protecting technology.
Protecting the organisation’s ability to operate, adapt and remain trusted.
Continue the discussion on LinkedIn